-
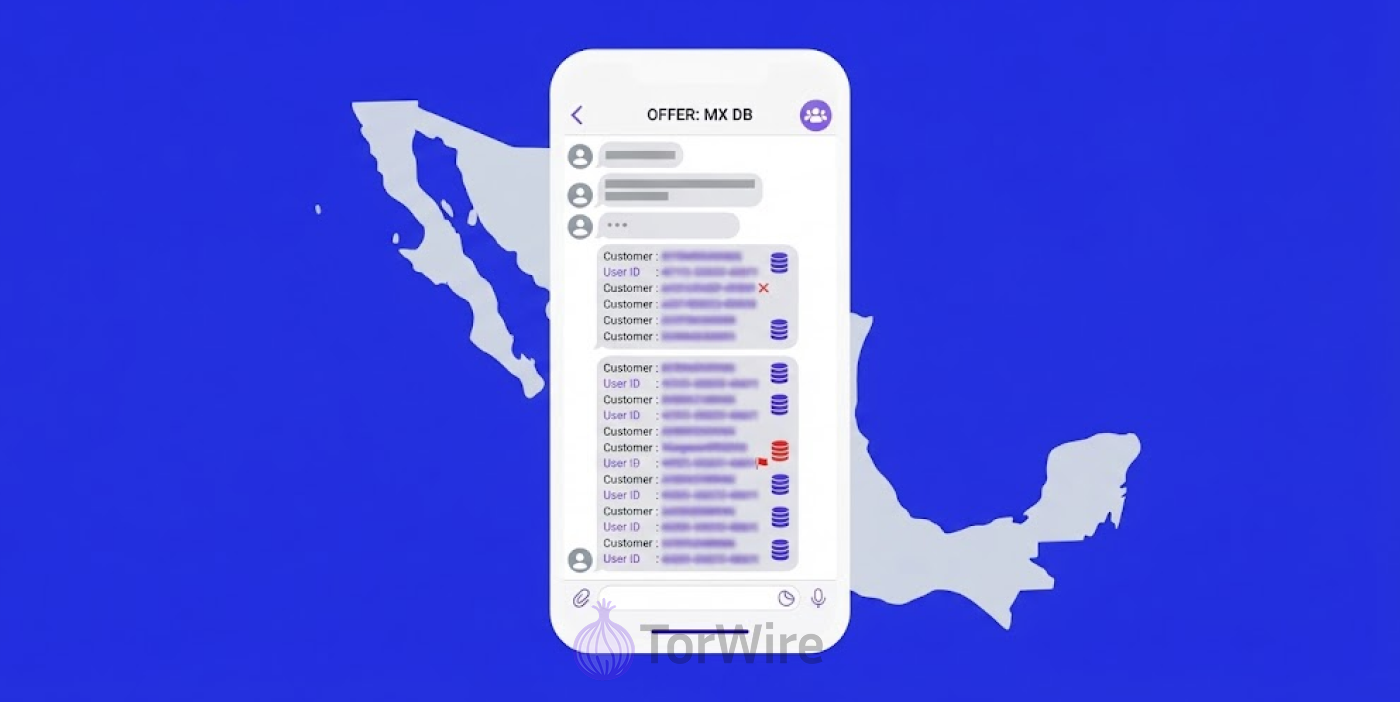
Mexico’s government says a Telegram seller offered more than 12.9 million records tied to various call centers.
-
A government sample contained data linked to major banks, retailers and other brands, but the source of each record remains under investigation.
-
Microsoft SharePoint flaw CVE-2026-65660 is under active exploitation, while SharePoint 2016 and 2019 reached end of support in July.
Mexico’s Secretariat of Anti-Corruption and Good Government said Sept. 24 that it had found a Telegram post offering more than 12.9 million personal records. According to reports, the agency found the post during active monitoring on Sept. 22.
The records were tied to several call center databases. The sample included names, email addresses, phone numbers, birth dates, RFC tax IDs, addresses, and banking information.
RFC is Mexico’s federal taxpayer identification number. The agency obtained 13,000 records from 13 databases. The sample contained names linked to Amazon, American Express, Afirme, Liverpool, Banamex, BBVA, HSBC, Inbursa, Banorte, Banregio, INVEX, Sam’s Club, Santander, Suburbia, Walmart, Scotiabank, Sears, Soriana and other companies.
That does not mean those companies suffered a direct breach. The government has not revealed whether the banks or retailers themselves suffered any breach. The records were associated with databases held by call centers. The agency said it will investigate who may be responsible.
The distinction matters. Companies often use outside providers for customer calls and support. A compromise at one provider can expose data from several businesses. The government has not identified the Telegram seller or confirmed how they obtained the databases. It also has not said every advertised record is genuine.
Why the Data Could Fuel Fraud
The data mix could make scam calls more convincing. A caller who knows a person’s name, phone number, address, birth date, and RFC can sound far more credible than a stranger with only a phone number.
That does not prove attackers will use these records. It does show why people should treat unexpected financial calls with care. A person claiming to represent a bank may already know several personal details. But that information alone is not enough to prove the caller’s legitimacy.
The most appropriate option would be to hang up and contact your bank using a reputable phone number. The Secretariat said it will review the sample and investigate possible violations of Mexico’s private-sector data protection law.
The Gentlemen lists Magnetos y Refacciones
Another event involving Mexico occurred in the same time period. The ransomware gang TheGentlemen listed Magnetos y Refacciones on its leak website.
Public threat intelligence databases have identified the company as one established in 1977 in Guadalajara. The company deals in the sale of electrical equipment, supplies, and repairs of motor parts.
However, the ransomware claim does not constitute evidence of a successful attack. There is a difference of opinion in public threat intelligence resources regarding the date of the leak, as it ranges between September 21 and September 26.
A tracker said there aren’t enough details to determine the type of stolen data. Also, there’s no report from the company confirming the ransomware claim.
This makes the situation different from the Telegram case. The Mexican government confirmed that it discovered the database sale advertisement and retrieved a sample. But the ransomware listing is still just an unverified claim at this point.
SharePoint Attacks Add Another Warning
Microsoft SharePoint users also face a fresh threat. CVE-2026-65660 is a code injection flaw that can let an authorized attacker execute code over a network.
This vulnerability impacts SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition. CISA included the vulnerability in the Known Exploited Vulnerabilities list on Sept. 25 based on confirmed exploits.
The Canadian Centre for Cyber Security also said it was aware of active exploitation. It warned that attackers can chain the flaw with other SharePoint weaknesses to achieve remote code execution before authentication on some systems.
Fixed builds are available. For SharePoint 2016, the patched version is 16.0.5565.1001. Version 16.0.10417.20198 is the patched version for SharePoint 2019. Subscription Edition is fixed in 16.0.19725.20522.
There is another problem for organizations still running the older products. SharePoint 2016 and 2019 reached end of life on July 15, 2026. That means organizations should not treat this as only a patching issue. They should also plan to move from unsupported versions.
A Busy Day for Mexico’s Cyber Defenses
The three incidents show different risks at once. The Telegram case involves a large alleged sale of personal data. Other threat actors have also made claims involving enormous volumes of allegedly stolen data, including the hacker claiming theft of 10 petabytes of data from China’s supercomputing center. On the other hand, the Magnetos case involves an unverified ransomware claim, while the SharePoint issue involves confirmed active exploitation. But each highlights the value of basic defenses.
Organizations need to examine third-party access, protect consumer data exposure, apply patches to internet-facing systems, and uninstall unsupported software. For consumers, the message is clear that a caller knowing your RFC, address, or birth date does not prove they are from your bank. Hang up and call the bank yourself.