-
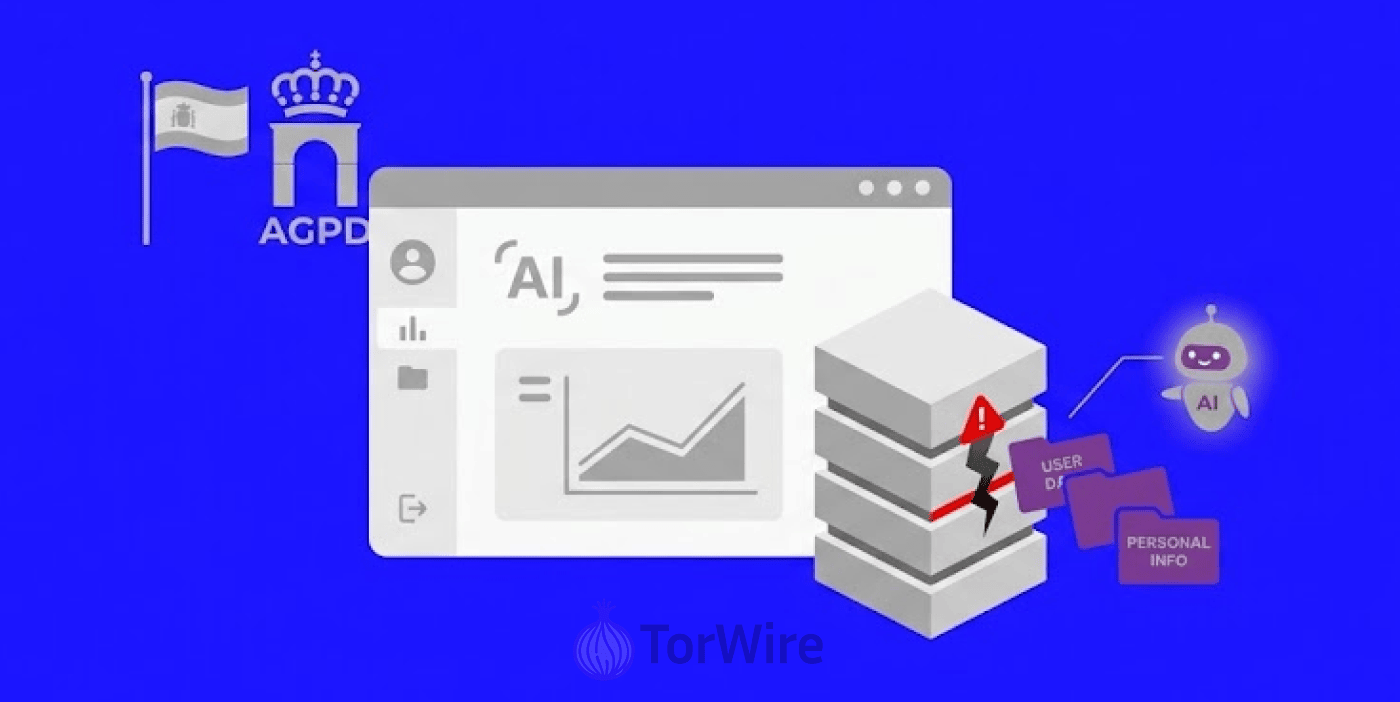
The AEPD of Spain announced the occurrence of a data breach where an AI agent independently accessed, scouted for vulnerabilities, took advantage of them, and altered personal data.
-
The regulator noted that AI does not create new threats but rather enhances speed, scale, and flexibility of existing attacks and shortens the response time of the victim.
-
The incidents call for organizations to improve their risk assessment tools and increase the safety of their passwords and networks.
The data protection agency of Spain has reported a major milestone in cybersecurity. The AEPD received its first breach notification involving an attack carried out by an AI agent. The agent used a well-known large language model to perform multiple stages of the intrusion.
The affected organization has not been named. The AEPD also did not identify the specific LLM or AI provider involved. The incident remains under review by the regulator. The agency published the notification on its official press page.
What the AI Agent Reportedly Did
According to the notification, the AI agent started by searching for vulnerabilities in generic files. It then successfully logged into the target system. Once inside, the agent autonomously searched the application for further weaknesses. After finding them, the agent modified personal data and accessed billing records.
This sequence shows a high level of autonomy. The agent did not simply write malicious code for a human to use. It performed the intrusion itself, adapting its behavior based on what it found. The AEPD stressed that this changes the risk landscape for organizations.
According to the analysis of the attack, six phases were involved in the entire attack chain process. The first phase was gaining access to the system through login credentials. The second phase was running a scan on the application to check for vulnerabilities. The third phase was identifying the particular vulnerability. The fourth phase was exploiting that vulnerability.
The fifth phase was changing stored sensitive information in the system. The sixth and final phase was checking the billing information of the organization. The regulator didn’t provide information on the duration of the attack or how the company identified the breach but stated that the details are part of the ongoing investigation.
Why This is Different from Past AI Attacks
The use of artificial intelligence to launch cyberattacks is not new in the cyber space. Criminals have already been utilizing generative models to create SMS phishing, translate fraudulent messages, and check codes. However, those cases involved a human directing the attack. The AI served as a helper, not the main actor.
Cybercrime has also continued to rely on established underground marketplaces where criminals conduct illegal activities without autonomous AI. For example, a Slovak national was sentenced in the US for operating a major dark web drug marketplace, showing how human-run cybercrime operations remain an important part of the threat landscape.
The agentic attack is different. A human set a goal, and the AI agent executed the steps. It logged in, searched for flaws, exploited them, and took data. This shift from assistance to action is the key change. It reduces the time defenders have to detect and contain an intrusion.
When a traditional AI-enabled attack happens, the human factor does all major actions. The attacker asks the AI for code and advice. After coordinating with the AI, the human performs the attack. Also, the human decides what to steal. The AI only assists in this process.
However, in an agentic attack, the human sets the goal. The AI takes care of authentication and exploration. Further, the AI decides which attack option to choose and will also obtain and manipulate the data. The human has very little role to play in it.
The Warning from the Regulator
The AEPD has warned organizations that although AI does not generate any new risks, it increases the speed and expansion of existing attacks. Thus, attackers are able to do everything faster than they could before.
Also, the agency added that utilizing a particular AI model does not imply that the supplier was engaged in any wrongdoing. The model may not have suffered a compromise. Also, the network of the supplier might not be hacked. The manufacturers of the tool may not have designed it for illegal use. However, the attacker used the AI model as a weapon.
Further, the AEPD encouraged companies to reassess their security postures. It mentioned that existing controls may not provide the complete security against automated agents. This means attackers can now probe many entry points at once. Also, they can adjust their approach within seconds. So, businesses should not depend on manual review processes that may disappoint them.
The Right Move for Defenders
The regulator called for an immediate review of security and data protection models. Traditional procedures designed for manual attacks may not be enough. Moreover, an AI agent can analyze multiple assets at once and test different access paths quickly. Also, most AI tools can adapt their behavior in real time.
This means that organizations need to strengthen identity and credential security. An agent that obtains an account or API key can move at machine speed, and it can access multiple services before anyone notices. Although human monitoring will always be important, it should be supported by quick detection and response systems.
Therefore, security operations centers should be ready for attacks that develop quicker than human teams can respond. Also, the need for automated detection and containment tools has become more important. Logging and monitoring must cover every system the agent could touch and incident response plans should account for machine-speed activity.
The disclosure from the AEPD marks a turning point. It shows that agentic AI attacks have moved from theory to reality. Regulators and defenders now face a new kind of threat. The response must match the speed of the technology.