-
ZachXBT says he put up $349,700 and took a planned 5% loss on every trade to get inside a Chinese network that launders crypto for North Korean hackers.
-
He claims the group cleaned more than $1 billion, including most of the $1.5 billion Bybit theft. His intel helped freeze some of that money.
-
No government has named ZachXBT’s main contact or confirmed the $1 billion figure. The claims remain unproven.
On October 5, onchain investigator ZachXBT said he infiltrated a Chinese organized crime group that launders stolen crypto for North Korea’s Lazarus Group. He posted a 12-part X thread describing the method he used to get inside the laundering network. According to the post, he posed as a customer and paid real money to earn trust. He says the group has washed more than $1 billion across several hacks.
How ZachXBT Found an Opening Into the Criminal Network
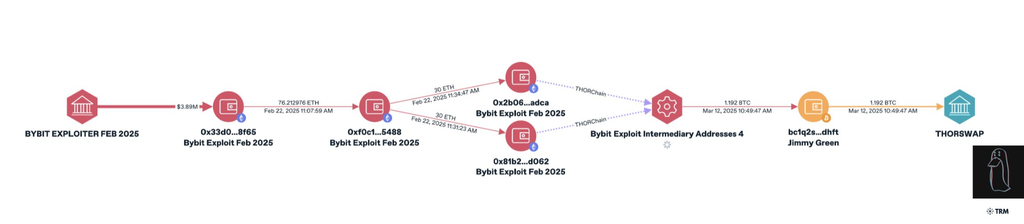
ZachXBT noticed a pattern after the $1.5 billion Bybit hack in February 2025. More than 15 accounts in public Telegram and Discord groups were asking for help with orders tied to stolen funds. They acted like ordinary users filing support tickets. He messaged several of them. One used the name ‘Jimmy Green’ on Telegram.
It’s worth noting that the FBI later blamed the Bybit theft on North Korea’s TraderTraitor team, also known as Lazarus Group. The agency said the attackers quickly spread the stolen assets across thousands of blockchain addresses. It also warned that the funds would likely move through additional services before conversion into traditional money.
Bybit also indicated through its forensics investigation that the Lazarus Group was behind the hack. It indicated that the hackers were able to steal access details of a Safe developer in order to fool transaction signers.
The blockchain analysis firm Chainalysis also noted that North Korean actors have often used laundering services for moving their stolen money. This helps understand ZachXBT’s claims. However, this is not sufficient enough to prove all the details from his undercover work.
Paying Money to Earn Trust
ZachXBT followed up with Jimmy Green. On March 6, 2025, ZachXBT funded a new Ethereum wallet with 349,700 USDC. Jimmy gave him an address and asked him to send the USDC in exchange for USDT on the Tron network.
ZachXBT says that address got its gas money from a wallet tied to the Bybit hack and listed on Bybit’s public illegal list. Then he ran several more trades to look like a reliable client. He chose to lose 5% on each order. He says Jimmy could have kept the money, and he accepted an unknown level of personal risk.
What ZachXBT’s Undercover Investigation Revealed
Once trust grew, Jimmy began talking. He described how his team moved Bybit money for North Korea. He also gave details about operations in Hong Kong and mainland China.
ZachXBT says Jimmy predicted a move to Solana one day before it happened. Jimmy claimed his team washed most of the $1.5 billion. That matched the laundering patterns ZachXBT had seen onchain.
In leaked Telegram messages, an alleged launderer wrote that Kim Jong-un was testing Bitcoin lately because he feared USDT freezes. Notably, Tether can freeze USDT, which makes it a risky choice for thieves.
On March 12, 2025, Jimmy shared a screenshot of himself bridging funds. ZachXBT matched the amount and timing to a THORChain transaction made minutes earlier.
Jimmy also shared three Solana addresses.
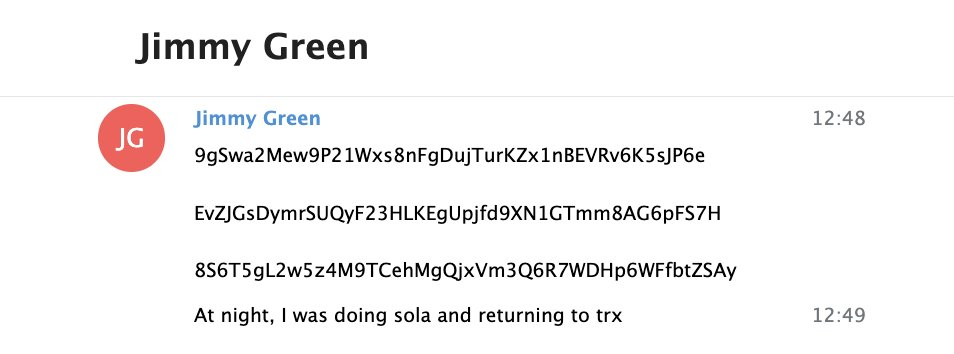
Those wallets held more than $12 million in Bybit funds, and ZachXBT watched the money hop from Bitcoin to Ether, then Solana, then Tron in real time.
Tether later froze about 442,000 USDT linked to that cluster. The cluster also tried a new trick. It used Uniswap liquidity pools filled with illiquid tokens to hide where the money came from.
Other Leads from Zach’s Chats with the Gang Member
Jimmy mentioned a team that had about $300,000 frozen in 2024. ZachXBT found the freeze onchain. The real figure was 332,000 USDC from the Poloniex exploit.
Jimmy also bragged about laundering $3 million in fraud money for another client. ZachXBT traced it to a hot wallet at Huione Guarantee. That matters because the US Treasury’s FinCEN found Huione Group laundered over $4 billion between August 2021 and January 2025, including $37 million from North Korean heists. Huione’s former chairman, Li Xiong, was extradited from Cambodia to China on April 1.
A Link to the Bitget Hack
ZachXBT tied this story to a newer case. On September 24, attackers drained about $387.5 million from the exchange Bitget. Its CEO said North Korea was very likely behind the theft. The method looked familiar. Like Bybit, the attackers did not need the exchange’s private keys.
Last week, ZachXBT said suspected launderers of those funds were also asking for help in public chat groups. ZachXBT has previously reported similar behavior from suspected Bitget hack launderers, as detailed in ZachXBT Says Bitget Hack Launderers Seek Help in Public Chat Rooms.
He flagged five accounts, and at least one was linked to the $292 million Kelp DAO exploit earlier this year. That suggests the same crews work on hack after hack.
North Korean Hackers’ Affinity for Chinese Middlemen
North Korean hackers are good at stealing. Turning the loot into spendable cash is harder, so they hire brokers. This is not new. In 2020, US prosecutors charged two Chinese nationals with laundering more than $100 million stolen by North Korean hackers from an exchange in 2018. ZachXBT’s thread suggests the same type of broker still does this work, and does it in plain sight.
What is Still Unproven
Official documents from the FBI, Treasury, and Tether have not named the person behind the Jimmy Green alias, and no court filings back the full scope of the network. The $1 billion total comes from ZachXBT and his reading of the chain data.
He did post wallet addresses, transaction hashes, and screenshots of his chats. Anyone can check the onchain parts. The identity of the people behind them is another matter.
ZachXBT says he has helped freeze more than $75 million tied to North Korean incidents since 2022. He says he gave his findings right away to trusted private-sector investigators and to law enforcement on the case. He held back from posting because of the sensitivity of the investigation.
ZachXBT ended his thread with a plea for funding. He wants grants from foundations and donations from individuals, since that money lets him take risks others avoid. Also, he says he is sitting on significant findings from other cases.
For now, the thread offers a rare look at how stolen crypto gets cleaned. The suspects were not hiding on the dark web. They were asking for support in public groups, and one of them ended up trading with an investigator.