-
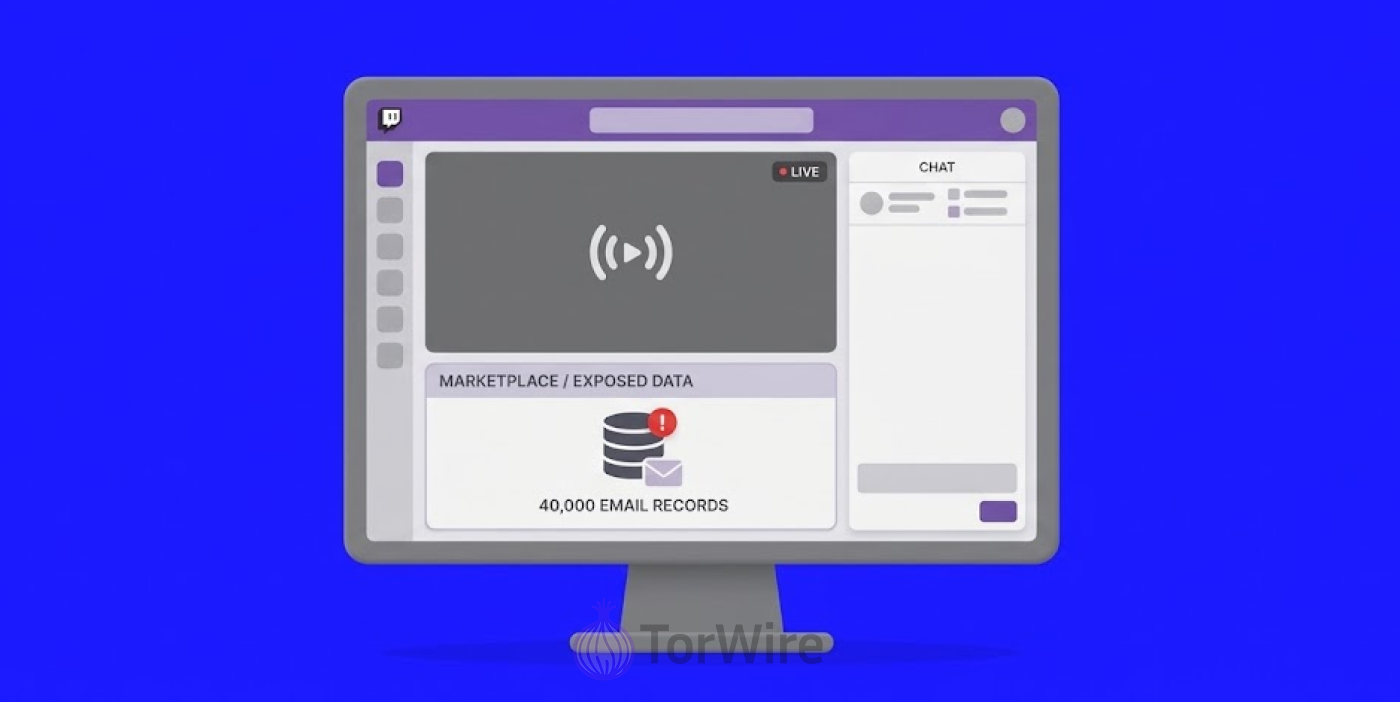
A seller claims to have personal data on almost 40,000 Twitch streamers, including emails, legal names, and follower counts.
-
Twitch itself shows no sign of a hack. The seller reportedly calls this data a “scrape,” not stolen goods.
-
Streamers linked to crypto content may face higher risks from targeted scams and phishing attempts.
A dataset allegedly holding personal details on nearly 40,000 Twitch streamers is reportedly up for sale. This raises fresh worries about how creator data gets collected and resold online.
Dark Web Intelligence shared the claim in a post on X. According to the alleged listing, the data includes Twitch usernames, profile links, email addresses, legal names, follower counts, and verification status. The seller reportedly says most emails belong to individuals, though some business addresses appear too.
Some streamers on the list reportedly work in the crypto space. That detail could make them easy targets for phishing attacks and other money-driven scams.
Seller Calls this a Scrape, Not a Hack
The seller allegedly describes this data as a “scrape.” That word matters a lot here. It suggests the information came from public sources, not a break-in at Twitch itself. Nothing available right now shows that Twitch’s own systems got breached. Nobody has confirmed exactly how the seller gathered this data either.
The seller reportedly claims the names and emails didn’t come only from streamer bios. This hints that other data sources got mixed in with public Twitch profile info, though nobody can confirm that part yet.
Databases like this already exist elsewhere online. Streams Charts tracks creator and streaming data across several platforms. StreamersDB lists thousands of Twitch streamers along with contact details. A separate tool, this Twitch email scraper on Apify, pulls public email addresses tied to Twitch channels. BizProspex even sells ready-made Twitch streamer contact lists.
None of these services can confirm or match the specific 40,000-record dataset mentioned in the alleged listing.
Crypto Streamers Could Face Bigger Risks
Even without a direct Twitch breach, this kind of data creates real danger. Linking a streamer’s legal name to their online identity raises serious privacy concerns.
Scammers could use this info to send convincing fake emails. They might pose as Twitch staff offering partnerships or sponsorship deals. They could also pretend an account faces suspension or needs urgent verification. Personal email addresses make it easier for attackers to reach streamers outside the Twitch platform entirely.
Attackers are targeting YouTube creators with fake copyright notices that mimic official emails and threaten channel termination. The messages link to fake Google support pages designed to steal login credentials. YouTube says it does not send copyright notices this way and advises creators to verify messages through YouTube Studio.
Crypto streamers face the sharpest edge of this risk. According to research on viewbotting and creator fraud, scammers already build detailed profiles before targeting creators. A leaked identity gives attackers a head start on crypto-related scams or fake investment pitches.
Exposing real names next to online usernames brings other problems too. Streamers could face harassment or doxxing from people who get hold of this list. That risk grows for anyone who keeps their real identity private for safety reasons.
Nobody Has Verified the Dataset Yet
Right now, this remains an alleged data exposure. It is not a confirmed breach of Twitch’s systems. The 40,000-record figure hasn’t been independently verified. The seller’s identity also remains unknown. The exact method used to collect the data still isn’t clear. No major cybersecurity outlet appears to have confirmed this specific claim as of this writing.
Even so, this case shows something important. Small pieces of public information can turn into valuable, dangerous datasets once someone combines them. A username here, an email there, a legal name somewhere else. None of it seems risky alone. Put together, it becomes a tool for targeted attacks.
Even when a platform like Twitch stays secure, outside data collection can still put creators at risk. Third-party scraping tools and marketing databases already gather this kind of information at scale, whether or not this exact dataset turns out to be real.
Streamers should stay alert for emails claiming to offer partnerships or sponsorship deals out of nowhere. They should double-check any message asking for account verification before clicking anything. Using a strong, unique password for Twitch and turning on two-factor authentication both help reduce risk. Crypto-focused streamers especially should treat unsolicited business offers with extra caution.
Stay careful with unexpected emails. Watch for anything asking for personal details or login information. And remember that even public data, once collected and packaged, can end up working against the very people it describes.