-
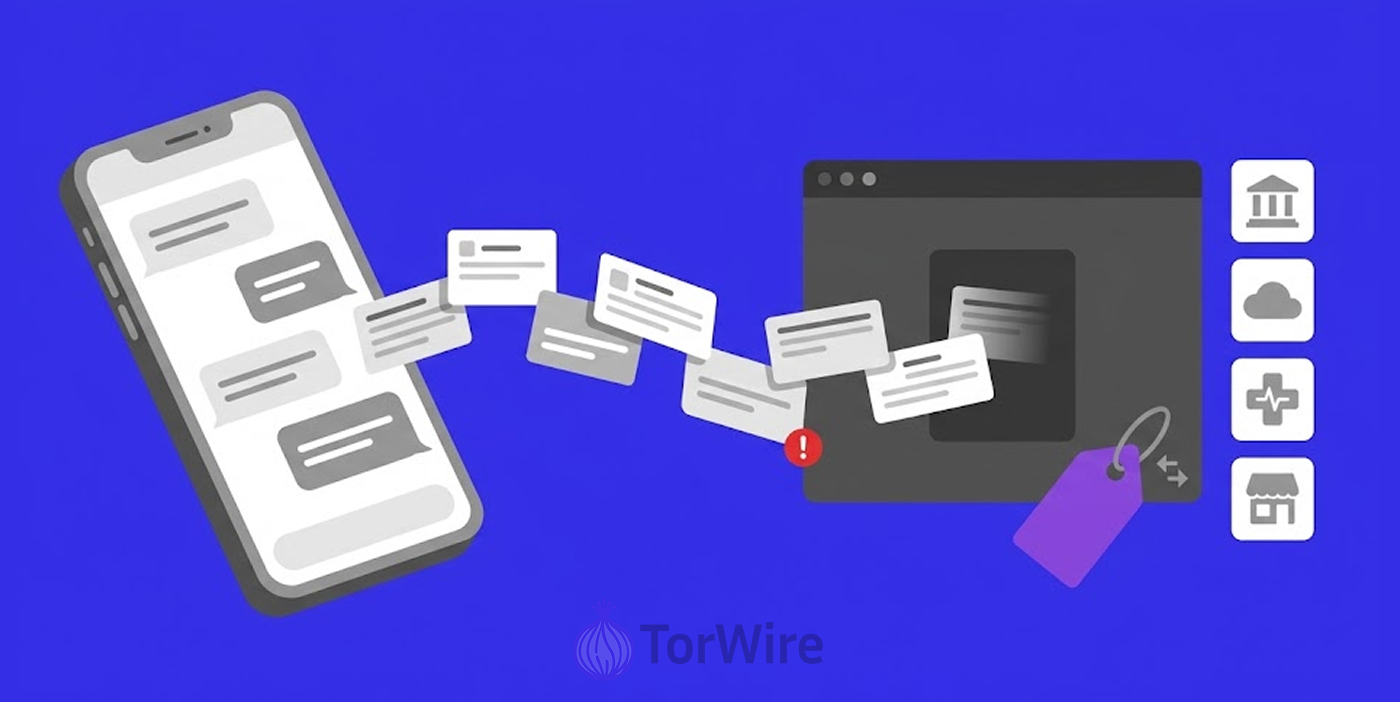
A forum seller says he holds text message logs tied to HeyDude India, SalaryBox, Astroyogi and Fragrant Souq.
-
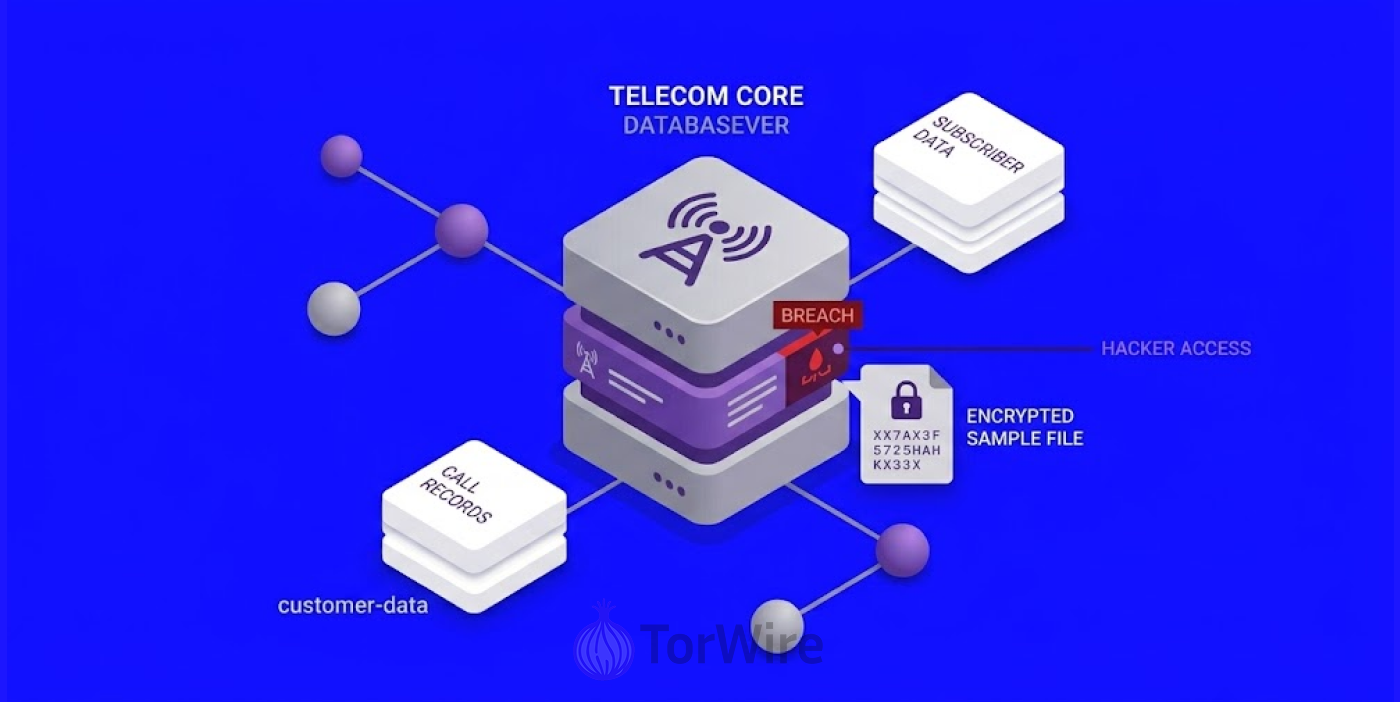
The seller provided four samples, and they all use the same log format. That probably means they’re from a single source, not from four separate breaches.
-
The listing claims the data contains phone numbers, order details, payroll data, even booking records. Stuff like this makes scam messages look much more convincing.
Someone on an underground forum is offering four datasets they claim are from popular brands for sale. The samples look like text message logs, not typical customer databases. Asking prices run from 1K to 3K per set. As of October 12, none of the companies have confirmed a problem.
The listings claim the following:
- 15 million records from HeyDude India, including names, mobile numbers and cart-reminder texts.
- 4 million records of renewal and attendance reminder texts SalaryBox.
- 2.9 million Astroyogi user records, including one-time passcodes and booking links.
- 110,000 records from Fragrant Souq, with customer names and order-confirmation texts.
The samples also show carrier names, delivery status and timestamps from mid-2026. But there’s currently no company statements or any earlier reports of these leaks validating the claims.
Which Brands Appear on the Listing
The listing names the site heydude.in, which points to HeyDude’s Indian outlet. HeyDude is a shoe company that Crocs purchased in 2022. The brand entered the Indian market in 2024 using Metro Brands and had 25 stores.
SalaryBox is a payroll and attendance app for small businesses. It is based in Gurugram and joined Y Combinator in 2021.
Astroyogi is the consumer brand of Netway India. The company says it began in 2001 by making content for telecom firms. One recent roundup says it serves more than 30 million users.
If so, the claimed 2.9 million records would cover a slice of them. There’s nothing about Fragrant Souq or any incident tying it to the recent claims.
One Provider is the Likely Suspect
Four unrelated companies rarely leak in the same format on the same day. A shared texting vendor is a simpler explanation. These companies send reminders and codes through outside gateways, and those gateways keep logs.
Past cases support the idea. In 2024, a Swedish vendor called SMS Teknik had its backup systems hit. The exposed data reportedly included communication logs, and its customers had to warn their own users. In 2018, the provider Voxox left millions of texts open online, including login codes. In 2019, TrueDialog exposed millions of business texts, with names, numbers and message content.
Another report examines an alleged stealer-log leak involving major technology companies and other global firms; it claims the leak includes data from Apple, Google, and dozens of other firms.
India has seen this before. Reports state carrier BSNL exposed about 278GB of data in two incidents, including SMS logs and call records. The organization acknowledged the issues and advised people to be careful about any suspicious messages. That shows message logs can leak at scale.
Still, this is a guess. Underground forum listings have a tendency to exaggerate figures and use old figures. Prices from 1K to 3K also imply that the seller does not want to negotiate. The mid-2026 dates make the samples look fresh, but dates can be edited.
Possible Risks of the Alleged Data Leak
Scammers do not have to know your password if they have a story to tell. It is difficult to recognize a scam text if it is associated with a certain order, payroll renewal or booking.
Research on UAE scams shows how this works. Security firm Group-IB tracked a gang that sent fake postal and toll texts there. Some recipients had never used the services named. Resecurity believed a similar gang may have bought personal data from breaches or the dark web.
One-time codes expire fast, so old ones are of little use. The main problem lies in the pattern. Logs show how different brands correspond with their clients.
Rules add pressure. One compliance guide says India treats mobile numbers and OTP delivery logs as personal data under its privacy law. Regulators are also moving away from SMS-only codes.
The Reserve Bank of India now requires stronger sign-in methods for domestic digital payments. The UAE central bank told banks to drop SMS and email codes by March 31, 2026.
What Customers and Companies Can Do
- Don’t click links in unexpected texts, even if they mention something you actually bought. Instead, just open the app yourself or type the website address in directly.
- Never hand out a code to anyone who hits you up first.
- Spot a fake message? Report it to your carrier or your local cybercrime portal.
And if you’re running a business, press your texting vendor for a straightforward answer. Did anyone get into your logs? Rotate gateway passwords and keys now. Check who has access to message history. Short retention periods help too, since old logs cannot leak if they are deleted.
For now, the priority is checking whether there’s a common vendor. If there is a common vendor, we may see more brands appearing. Watch out for news from the four companies and any provider that has shared messaging with them. Until then, you should view this list as a claim and not as a confirmed breach.