-
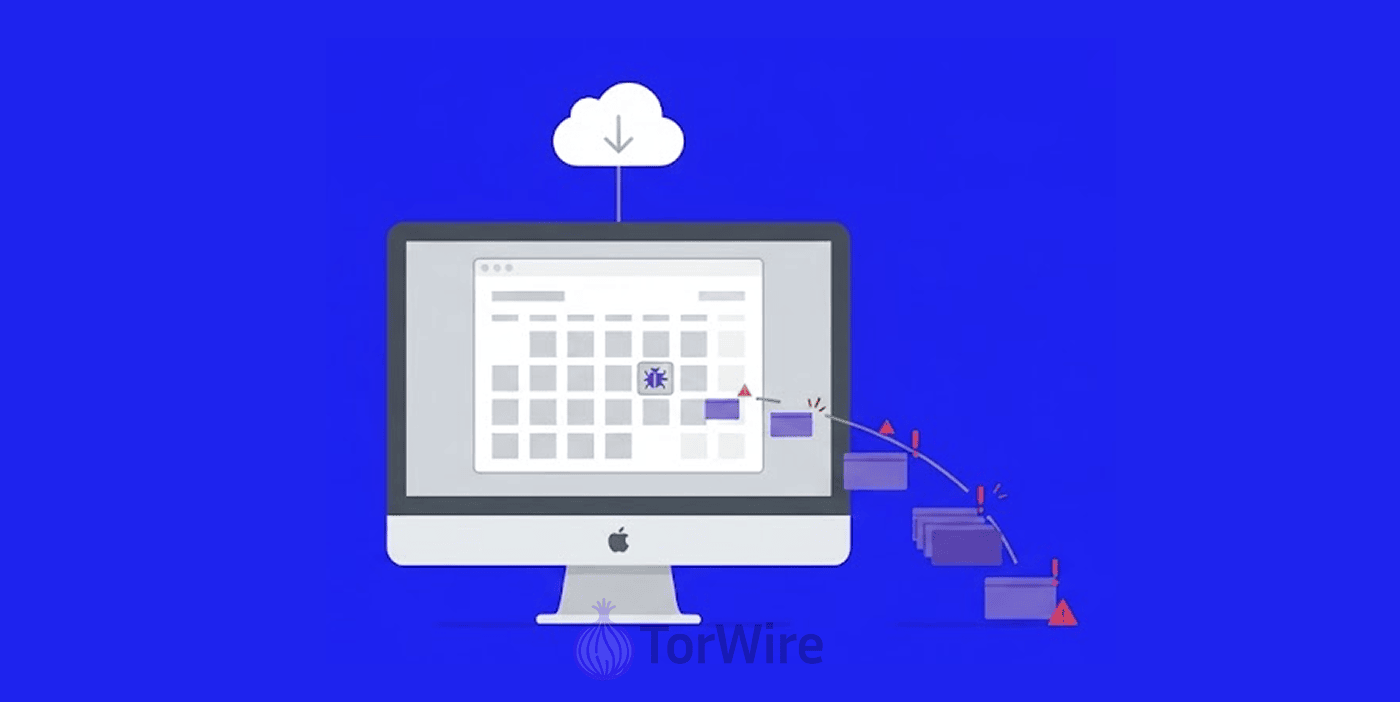
A newer version of MacSync malware hides attack commands inside public iCloud calendar events.
-
The malware now carries a backdoor that disguises itself as Finder, the Mac file manager.
-
Kaspersky says MacSync steals passwords, crypto wallets, browser data, and other private information.
Mac users are facing a sneakier threat this week. Security researchers at Kaspersky found a new version of the MacSync infostealer. It now uses a clever trick to spread further. The malware hides its commands inside public iCloud calendar events. This lets attackers sneak past normal security checks. Apple’s own servers end up hosting part of the attack chain.
MacSync first appeared around 2024 and 2025. According to Kaspersky, the malware has grown a lot since its early days. It shares roots with the AMOS stealer family, but this version does much more. The latest campaign pairs an infostealer with a brand-new backdoor. Attackers spread it through fake apps, social engineering, and ClickFix-style tricks.
Hackers Hide Commands Inside iCloud Calendar Events
The attack usually starts with a fake app download. Victims think they are installing real software. Kaspersky found examples like fake file-sharing tools and fake crypto wallets. One campaign pushed a bogus wallet app called Toria. People trusted the name and installed it without checking.
In a more advanced version of the attack, a small downloader fetches a public iCloud calendar file. That calendar file looks harmless at first glance. But hidden inside the event’s description field sit secret commands. These commands get passed straight to the Mac’s command line tool, called Z shell.
Most of the calendar text just creates error messages. It isn’t valid computer code, so the system ignores it. But a few lines placed after the description field actually run. Those lines quietly download an archive filled with more malware pieces, according to BleepingComputer.
That downloaded archive contains an app bundle. This bundle acts as a dropper, opening the door for later stages. Eventually, it installs the full MacSync payload onto the victim’s Mac. By using Apple’s own calendar service, hackers get free, trusted hosting. Their traffic blends in with normal iCloud activity, making it harder to catch.
A New Backdoor Gives MacSync More Power
The updated MacSync also brings a new backdoor built with Objective-C. It disguises itself as Finder, the app every Mac uses to manage files. Because the name looks familiar, most users never suspect a thing. Kaspersky found that this backdoor sets up long-term access in several ways.
It uses LaunchAgents, edits the .zshrc file, and adds global Git hooks. These methods let it restart automatically, even after the computer reboots. It can also shut down notification processes to hide warning pop-ups.
The older infostealer part still works too. It grabs browser history, saved cookies, and stored passwords. It also targets crypto wallet files, Telegram data, and the Mac Keychain. On top of that, it searches for SSH keys, AWS logins, Kubernetes files, and Git settings.
The new backdoor adds even more danger. It can receive AppleScript commands straight from the attacker’s control server. It gathers files and system details from the infected Mac. It can install browser extensions without asking permission.
It can even replace a real Ledger wallet app with a fake one built by the attackers. Kaspersky also spotted a command called live_browser. Researchers admit they still don’t fully know what that command downloads or does, according to Kaspersky’s report.
How Mac Users Can Stay Safe
Kaspersky shared a few simple steps Mac users can take right away. Avoid running any command copied from a website you don’t fully trust. Be extra careful with DMG files downloaded from random or suspicious sources. Pay close attention whenever your Mac asks for an admin password unexpectedly.
Apple users also face phishing campaigns that use fake security warnings to trick victims into handing over sensitive account information, as covered in phishing scams that use fake Apple security alerts to steal iCloud credentials. If a prompt feels off or appears out of nowhere, stop and check it first.
This case shows a bigger pattern in how attackers now operate. They mix social tricks with trusted cloud platforms to slip past defenses. Using Apple’s iCloud calendars makes malicious traffic look like everyday activity. That makes the attack far harder for regular security tools to catch.
Kaspersky and other researchers continue to track MacSync as it evolves. For now, no wide-scale outbreak has been confirmed publicly. But the techniques used here, hiding code inside trusted services, could easily spread to other platforms. Staying alert to unusual downloads and unexpected prompts remains the strongest defense.